DOWNLOAD the newest Exam-Killer JN0-336 PDF dumps from Cloud Storage for free: https://drive.google.com/open?id=1MwmQ_YhUDugXZ3uWb9J-v54mUoQQaBzd
Whatever exam you choose to take, Exam-Killer training dumps will be very helpful to you. Because all questions in the Actual JN0-336 Test are included in Exam-Killer practice test dumps which provide you with the adequate explanation that let you understand these questions well. As long as you master these questions and answers, you will sail through the exam you want to attend.
Juniper JN0-336 Exam Syllabus Topics:
| Section | Objectives |
|---|---|
| Identity-Aware Security Policies | - Identity concepts
|
| Intrusion Detection and Prevention (IDP) | - IDP concepts and architecture
|
| IPsec VPN | - IPsec fundamentals and deployment
|
| Security Director (Junos Space) | - Management platform
|
| High Availability (HA) Clustering | - Chassis cluster operations
|
| Juniper Advanced Threat Prevention (ATP) Cloud | - Operations
|
| SSL Proxy | - SSL inspection concepts
|
>> New Study JN0-336 Questions <<
Pass Guaranteed 2026 Juniper JN0-336: Security, Specialist (JNCIS-SEC) Pass-Sure New Study Questions
As everybody knows, competitions appear ubiquitously in current society. In order to live a better live, people improve themselves by furthering their study, as well as increase their professional JN0-336 skills. Once you purchase our JN0-336 exam material, your time and energy will reach a maximum utilization. Thus at that time, you would not need to afraid of the cruel society and peer pressure with JN0-336 Certification. In conclusion, a career enables you to live a fuller and safer life. So if you want to take an upper hand and get a well-pleasing career our JN0-336 learning question would be your best friend.
Juniper Security, Specialist (JNCIS-SEC) Sample Questions (Q55-Q60):
NEW QUESTION # 55
You are asked to configure your company SRX Series device to use identity-aware security policies.
Information about your Active Directory network is shown in the exhibit.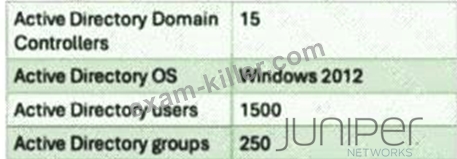
In this scenario, why must you configure JIMS instead of Active Directory as an identity source?
- A. You have too many domain controllers.
- B. JIMS is the only way to get data from Active Directory.
- C. The version of Windows OS is too old.
- D. You have too many Active Directory users.
Answer: A
Explanation:
The correct answer is D. You have too many domain controllers. The exhibit shows 15 Active Directory domain controllers. Juniper's integrated Active Directory identity-source configuration for SRX identity- aware firewall supports a limited number of domain controllers; Juniper documentation states that an SRX Series device can configure a maximum of 10 domain controllers for Active Directory identity-source integration. Because this environment has 15 domain controllers, the direct Active Directory identity-source method exceeds the supported scale and JIMS must be used instead.
Option A is wrong because SRX devices can use Active Directory directly as an identity source; JIMS is not the only possible method. Option B is wrong because 1,500 users does not exceed the relevant identity-source scale shown here; Juniper documentation also notes probe functionality support well above this number.
Option C is wrong because the issue being tested is not the Windows Server version. JIMS is designed for larger identity-aware deployments and can centralize identity collection from Active Directory, domain controllers, Exchange servers, and syslog sources, then provide identity mappings to SRX firewalls. Juniper's JIMS datasheet shows much higher scale, including up to 100 active directories, 25 domains, and 500,000 user entries. Reference topics: Identity-Aware Security Policies, Active Directory identity source limits, JIMS scalability, domain controller scale limitations.
NEW QUESTION # 56
Which two statements are true about Juniper ATP Cloud? (Choose two.)
- A. Juniper ATP Cloud does not use antivirus software packages to protect against zero-day threats.
- B. Juniper ATP Cloud uses antivirus software packages to protect against zero-day threats.
- C. Juniper ATP Cloud uses multiple antivirus software packages to analyze files.
- D. Juniper ATP Cloud only uses one antivirus software package to analyze files.
Answer: A,C
Explanation:
Two statements that are true about Juniper ATP Cloud are:
Juniper ATP Cloud uses multiple antivirus software packages to analyze files: Juniper ATP Cloud is a cloud-based service that provides advanced threat prevention and detection for your network. It integrates with SRX Series firewalls and MX Series routers to analyze files and network traffic for signs of malicious activity. Juniper ATP Cloud uses multiple antivirus software packages from different vendors to scan files for known malware signatures and provide a comprehensive verdict based on their results.
Juniper ATP Cloud does not use antivirus software packages to protect against zero-day threats: Juniper ATP Cloud protects against zero-day threats by using dynamic analysis, not antivirus software packages.
Dynamic analysis is a method of executing files in a sandbox environment and observing their behavior and network interactions. Dynamic analysis can uncover unknown malware that may evade static analysis or signature-based detection methods.
Reference: = Juniper Advanced Threat Prevention Cloud (ATP Cloud), Juniper Advanced Threat Prevention Cloud | ATP Cloud | Juniper Networks, Breaking Down Security Complexity with Juniper Networks' ATP Cloud
NEW QUESTION # 57
Which two statements are correct about cluster components? (Choose two.)
- A. Cluster ID values are either 0 or 1.
- B. Cluster ID values range from 1 through 255.
- C. Node ID values range from 1 through 255.
- D. Node ID values are either 0 or 1.
Answer: B,D
Explanation:
The correct answers are A and B. In an SRX chassis cluster, the cluster ID identifies the chassis cluster itself, while the node ID identifies the individual SRX device inside that two-node cluster. Juniper states that a cluster is identified by a cluster-id value from 1 through 255, and that setting the cluster ID to 0 is equivalent to disabling clustering. Therefore, option A is correct and option C is wrong.
Option B is also correct because Juniper states that a cluster node is identified by a node ID specified as a number from 0 through 1. A normal SRX chassis cluster has two nodes: node0 and node1. The two devices must use the same nonzero cluster ID so they belong to the same cluster, but each device must use a different node ID so Junos can apply node-specific configuration, interface numbering, redundancy-group ownership, and management settings correctly. Option D is wrong because node IDs do not range from 1 through 255; that range applies to cluster IDs, not node IDs. Reference topics: HA Clustering, cluster ID, node ID, chassis cluster formation, node0/node1 identification.
NEW QUESTION # 58
Which two statements about SRX Series device chassis clusters are true? (Choose two.)
- A. Each chassis cluster member requires a unique cluster ID value.
- B. Chassis cluster member devices must be the same model.
- C. Each chassis cluster member device can host active redundancy groups
- D. Redundancy group 0 is only active on the cluster backup node.
Answer: B,C
Explanation:
In a chassis cluster, both nodes can host active redundancy groups. The active redundancy groups can be distributed between the two nodes, depending on the configuration and failover status, allowing each node to handle traffic for different sets of services or interfaces.
For the chassis clustering to function correctly, both nodes in the cluster must be of the same model.
This requirement ensures that the hardware capabilities, such as processing power and interface compatibility, are identical, which is crucial for maintaining consistent performance and behavior between cluster nodes.
NEW QUESTION # 59
Exhibit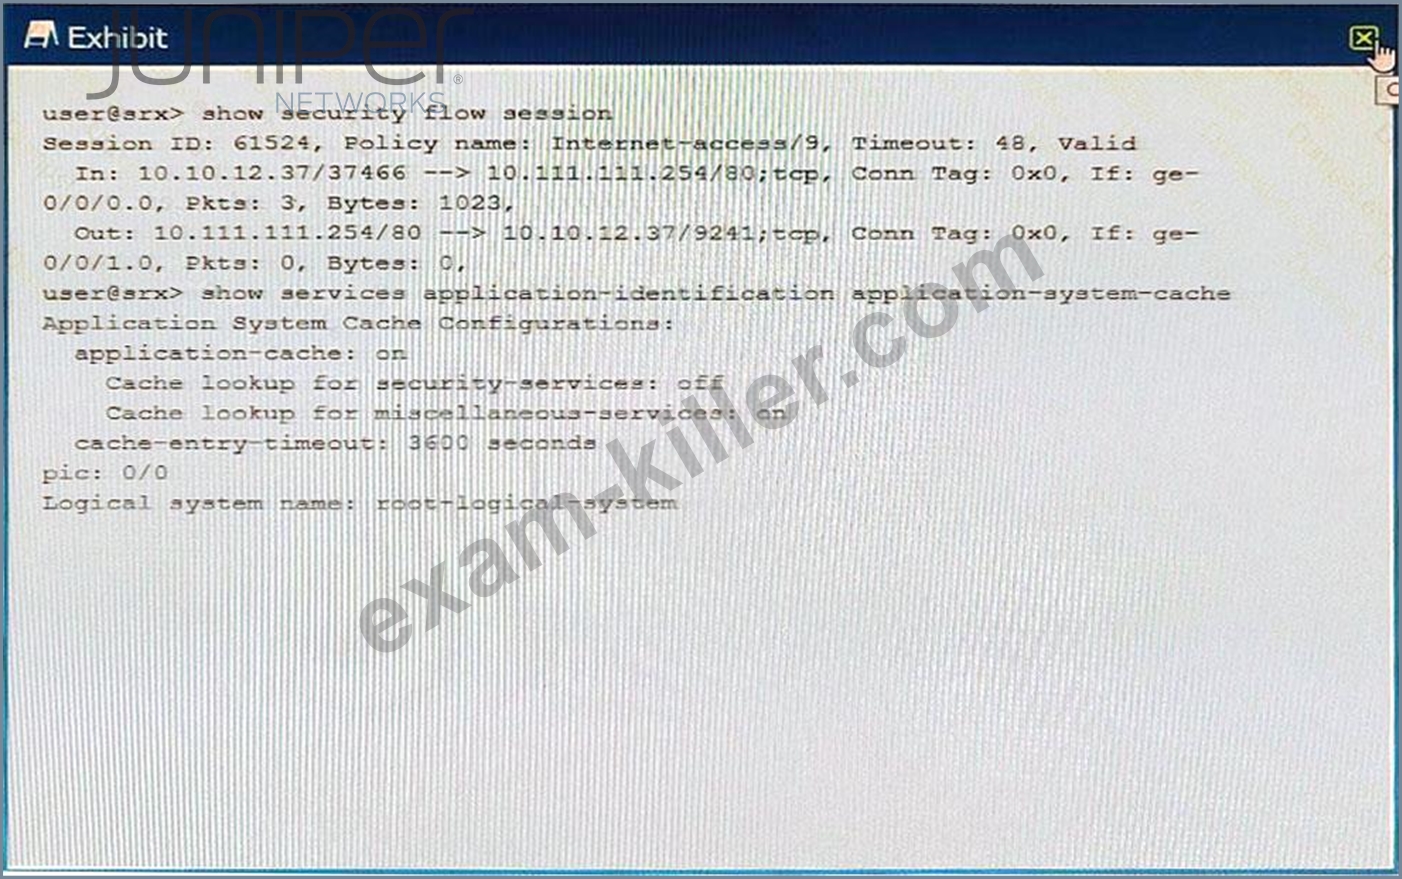
Referring to the exhibit which statement is true?
- A. SSL proxy leverages post-match results.
- B. SSL proxy leverages pre-match result
- C. SSL proxy must wait for return traffic for the final match to occur.
- D. SSL proxy functions will ignore the session.
Answer: C
NEW QUESTION # 60
......
However, you should keep in mind to pass the Security, Specialist (JNCIS-SEC) (JN0-336) certification exam is not an easy task. It is a challenging job. If you want to pass the JN0-336 exam then you have to put in some extra effort, time, and investment then you will be confident to pass the Security, Specialist (JNCIS-SEC) (JN0-336) exam. With the complete and comprehensive Security, Specialist (JNCIS-SEC) (JN0-336) exam dumps preparation you can pass the Security, Specialist (JNCIS-SEC) (JN0-336) exam with good scores. The Exam-Killer JN0-336 Questions can be helpful in this regard. You must try this.
JN0-336 Free Exam Questions: https://www.exam-killer.com/JN0-336-valid-questions.html
- Pass JN0-336 Guaranteed 🕝 Reliable JN0-336 Test Tips 🍺 Exam JN0-336 Voucher 👇 Go to website 「 www.practicevce.com 」 open and search for ➠ JN0-336 🠰 to download for free 🏨Exam JN0-336 Torrent
- New JN0-336 Study Notes 🦳 Valid JN0-336 Test Sample 🥺 JN0-336 Reliable Exam Review 📱 Easily obtain free download of ➥ JN0-336 🡄 by searching on ➡ www.pdfvce.com ️⬅️ 🌀JN0-336 Materials
- Exam JN0-336 Torrent 👮 JN0-336 Latest Exam Format 🏩 JN0-336 Exam Cram Questions ⌚ Search on ▷ www.practicevce.com ◁ for 【 JN0-336 】 to obtain exam materials for free download 👳JN0-336 Exam Cram Questions
- JN0-336 Troytec: Security, Specialist (JNCIS-SEC) - Juniper JN0-336 dumps 🟧 ➡ www.pdfvce.com ️⬅️ is best website to obtain ➠ JN0-336 🠰 for free download 🔟Reliable JN0-336 Exam Price
- Practice JN0-336 Mock 🥻 Practice JN0-336 Mock 🎺 New JN0-336 Dumps 🤲 Open website ☀ www.examcollectionpass.com ️☀️ and search for ⇛ JN0-336 ⇚ for free download 🦓New JN0-336 Test Objectives
- Free PDF Useful Juniper - JN0-336 - New Study Security, Specialist (JNCIS-SEC) Questions 🐞 Search for 「 JN0-336 」 and download it for free on ▛ www.pdfvce.com ▟ website 😗JN0-336 Reliable Test Tutorial
- 100% Pass Quiz 2026 Juniper JN0-336: Valid New Study Security, Specialist (JNCIS-SEC) Questions 📡 Search for 【 JN0-336 】 and download exam materials for free through ➤ www.prep4sures.top ⮘ 🧶Practice JN0-336 Mock
- Reliable JN0-336 Test Tips 😀 Reliable JN0-336 Test Tips 🛷 JN0-336 Test Questions Fee 🏸 Go to website ▶ www.pdfvce.com ◀ open and search for ⏩ JN0-336 ⏪ to download for free 🧾New JN0-336 Study Notes
- Security, Specialist (JNCIS-SEC) certkingdom actual exam dumps - JN0-336 pdf practice 📎 ✔ www.prepawayete.com ️✔️ is best website to obtain ➠ JN0-336 🠰 for free download 🍑Reliable JN0-336 Exam Price
- Juniper JN0-336 Exam Dumps - Pass Exam With Brilliant Score 🚏 Simply search for ▛ JN0-336 ▟ for free download on ➡ www.pdfvce.com ️⬅️ 🕣JN0-336 Reliable Exam Review
- JN0-336 Materials 👆 JN0-336 Latest Exam Format 🧯 Reliable JN0-336 Test Tips 🏖 Search for ➤ JN0-336 ⮘ and download exam materials for free through ➽ www.testkingpass.com 🢪 🍉JN0-336 Materials
- www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, myspace.com, www.stes.tyc.edu.tw, ccitonline.com, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, Disposable vapes
BONUS!!! Download part of Exam-Killer JN0-336 dumps for free: https://drive.google.com/open?id=1MwmQ_YhUDugXZ3uWb9J-v54mUoQQaBzd
Powered by